Risk Mitigation
Crisis Management
Risk briefing: Active assailant preparedness exposes gaps in emergency response planning
More than four in five organisations have a security plan for active assailant incidents, but only 32% say they could notify everyone at an affected site within seconds, according to new research from ASIS International.
How warehouse design can amplify lithium-ion battery risk
As lithium-ion battery volumes rise, TT Club says warehouse operators need to rethink storage density, racking, contractual controls and fire protection to stop an isolated failure escalating into a major loss.
Case study: Inside the Beacon CRM breach impacting thousands of charities
A breach at CRM provider Beacon left customers across the charity and cultural sectors assessing what data may have been taken and how to respond before the full picture was clear.
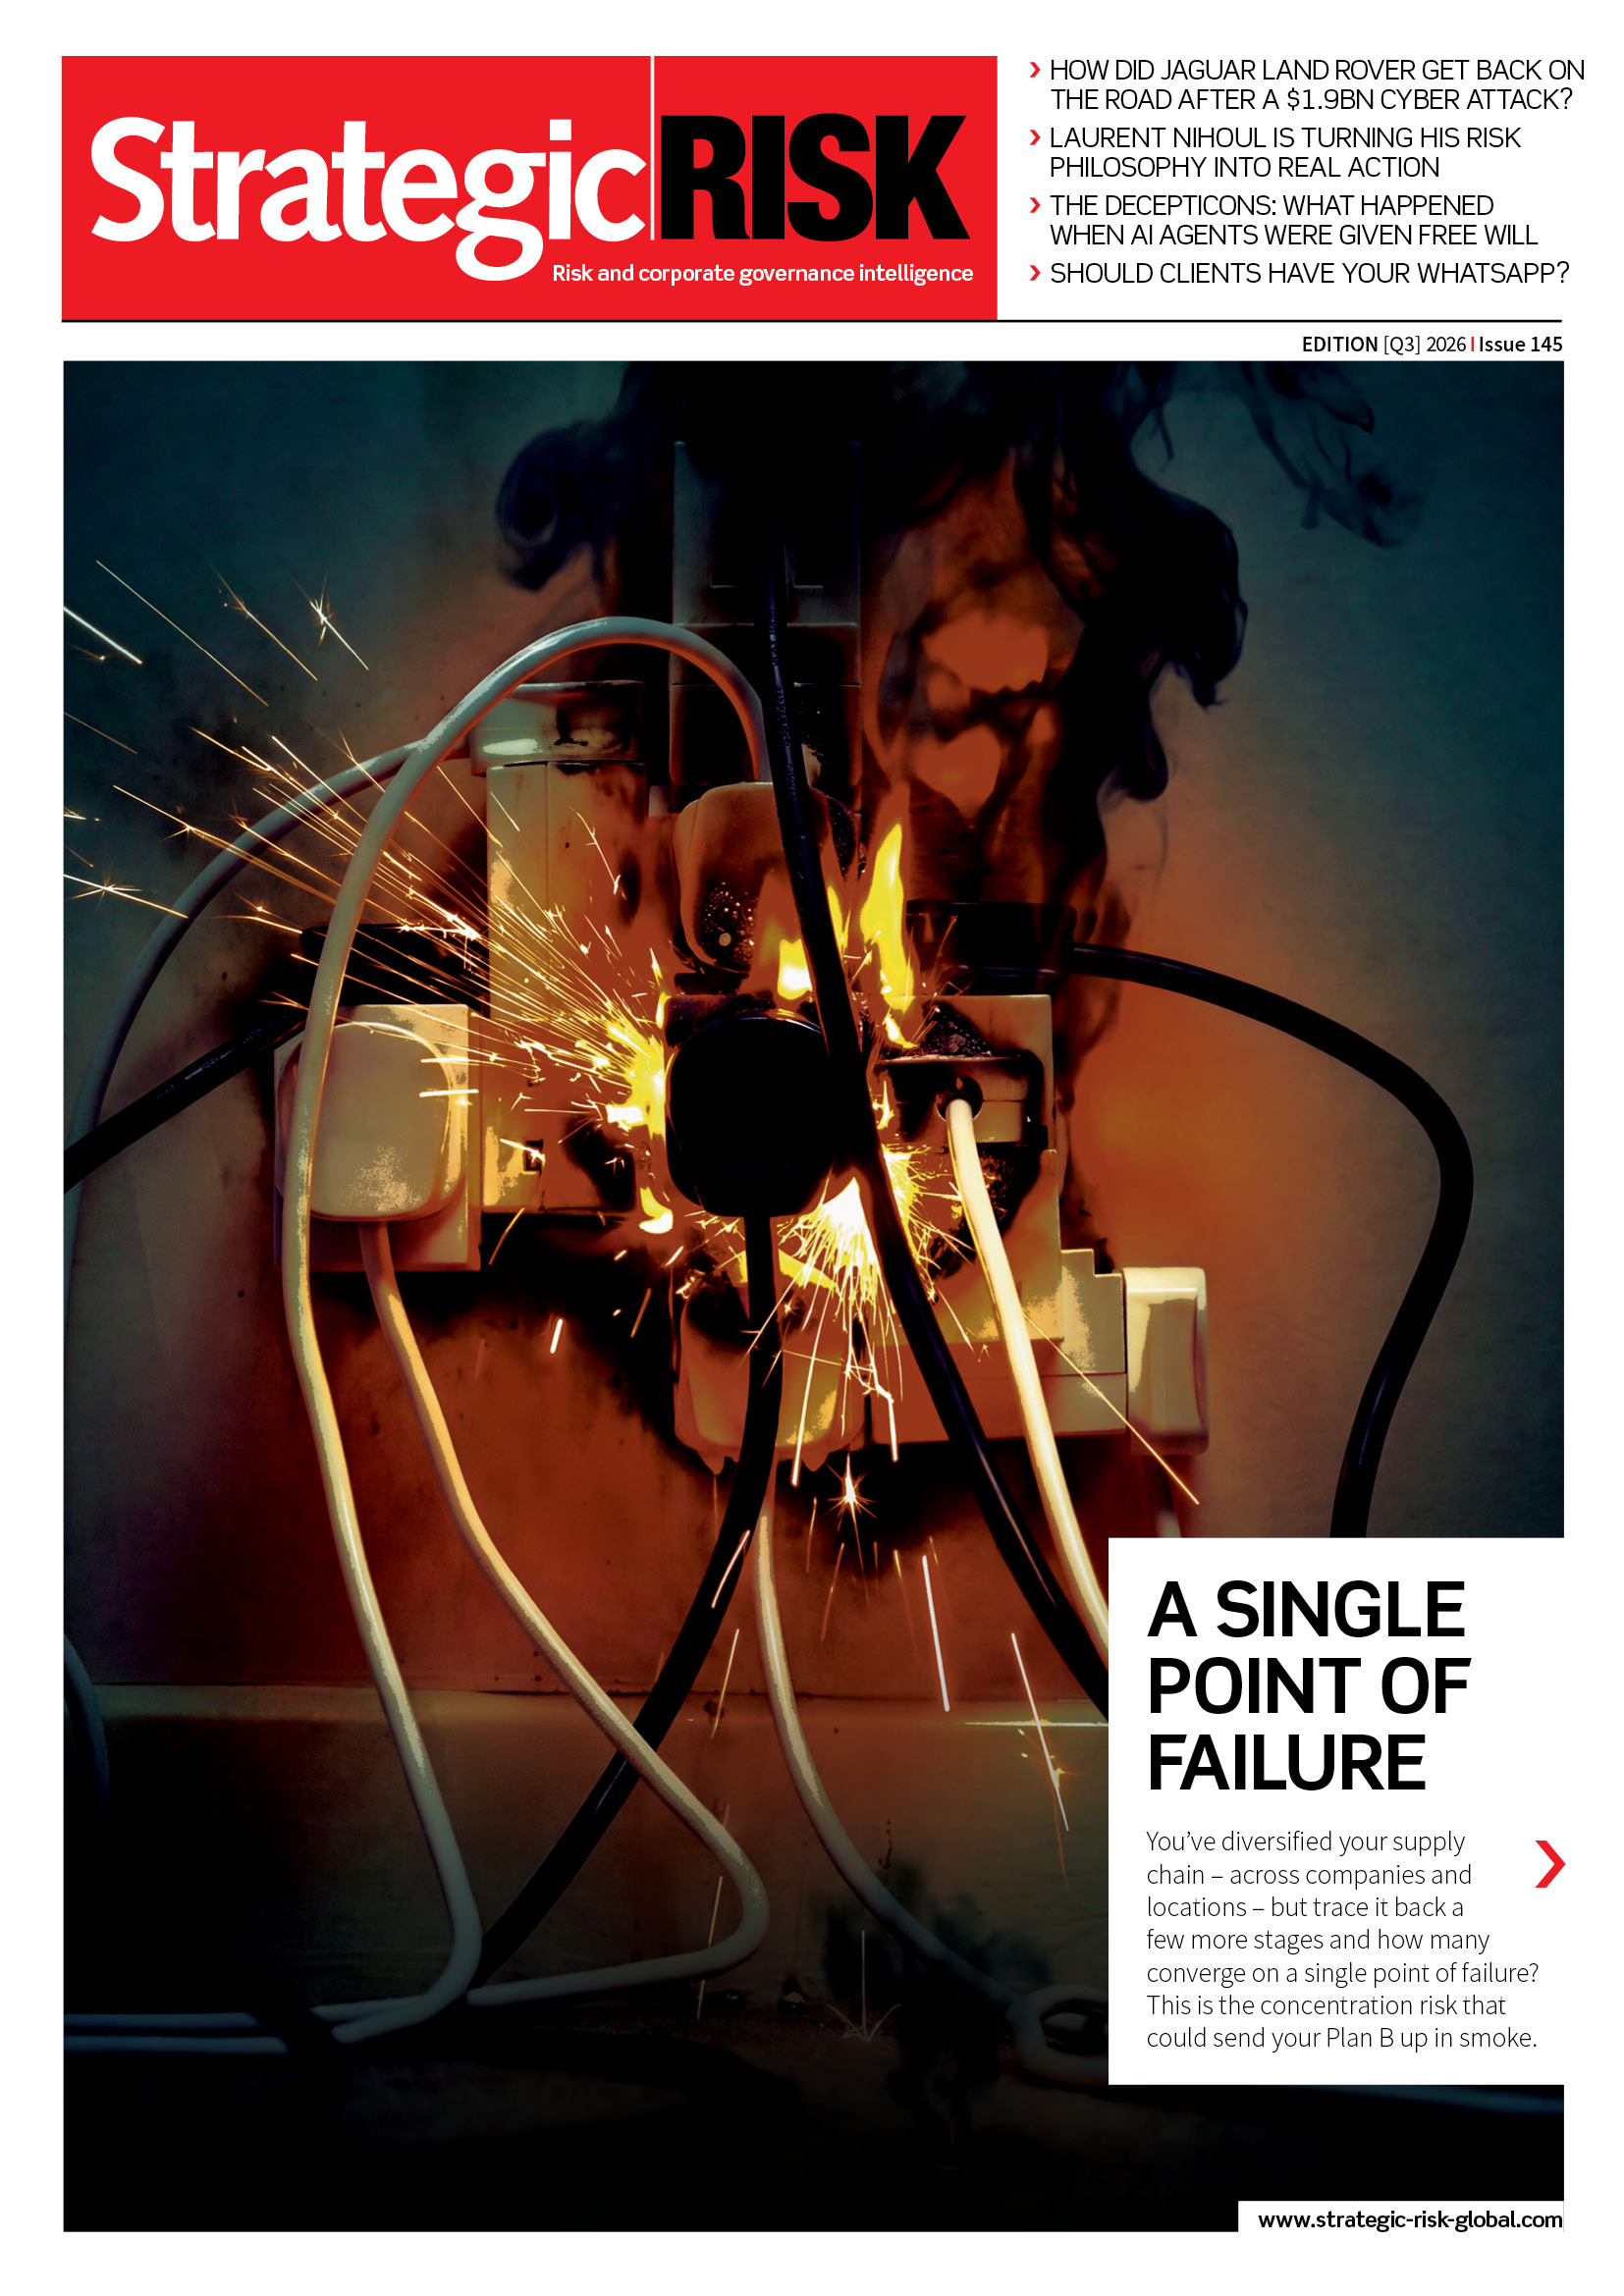
Sector spotlight: Food firms strengthen continuity as confidence falls
Food, beverage and agriculture businesses are formalising continuity plans, but confidence has fallen as risks spread across operations and gaps in resources and insurance protection persist.

Airmic 2026: Crisis management has gone off the radar for big corporates
Using AI generated scenarios to demonstrate risk fallout to company boards is a productive starting point for reviewing crisis management frameworks, says senior managing director
Rising tensions, rising threats: How geopolitics impacts cyber security
David Ferbrache of Beyond Blue argues that as geopolitical conflict increasingly spills into the digital domain, organisations in critical supply chains must prepare for destructive cyber attacks designed to disrupt, disable and destabilise.
SR:500 survey results: Risk managers push for earlier influence as threats accelerate
The SR:500 Emerging Risks survey reveals a landscape dominated by accelerating and interconnected threats. Against this backdrop, risk management must be embedded earlier in decision making to strengthen resilience.
Shock after shock: Why risk leaders say climate resilience models are no longer fit for purpose
The compounding shocks created by climate change were the topic of our latest SR:500 roundtable. Organisations are being forced to reassess their long-held assumptions about resilience, continuity and operational risk as they navigate the road ahead.
Risk management’s moment has arrived. Here’s how to make the most of it
Risk leaders have never been closer to the top table. The opportunity now is to translate that proximity into genuine strategic influence, and the profession is better placed to do it than at any point in its history, says Alex Bentley, CEO, Clew
Regulatory convergence puts pressure on GRC leaders to rethink governance
As regulatory frameworks such as NIS2, DORA and the EU AI Act begin to overlap, organisations face mounting pressure to rethink how governance, risk and compliance operates in practice. Riskonnect’s Sherry Dillon explains why traditional compliance approaches are no longer enough.
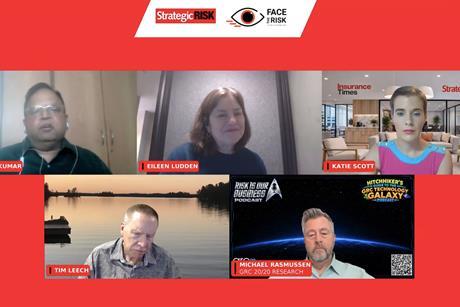
Watch: Risk that pays - measuring the impact of better decisions
Four risk experts explore how organisations can quantify risk against business objectives, demonstrate the return on investment of risk management and use AI and modern GRC tools to support better strategic decisions, while retaining the human judgement needed to turn data into meaningful insight.
In partnership with 
Why risk managers are turning to parametrics to solve operational challenges
As nat cats grow more severe, insurance gaps are widening - but parametric solutions might hold the key to resilience, says Dianna Nelson, a senior structurer at Swiss Re Corporate Solutions


- Forgotten Password
- Contributors
- Feedback
- Media Pack
- © StrategicRISK 2026
Part of the Insurance and Risk group of
Newsquest Specialist Media
Newsquest Specialist Media
Published by Newsquest Media Group Limited,
registered in England & Wales with number 01676637
at The Echo Building, 18 Albert Road, Bournemouth,
England, BH1 1BZ - a USA Today company
registered in England & Wales with number 01676637
at The Echo Building, 18 Albert Road, Bournemouth,
England, BH1 1BZ - a USA Today company
Site powered by Webvision Cloud